Wednesday, April 18, 2007

Virginia Tech and Wireless Access

A recent news article from eWeek.com indicates the there were wireless access problems at Virginia Tech on Monday. As you might expect, there were massive increases in the number of wireless voice calls and text messaging during the crisis, especially between 9:00 am and 2:00 pm. Verizon acknowledged some calls were blocked, but most text messages went through. Cingular claims no calls were blocked. Sprint Nextel also claimed no service interruptions despite the increased volume.

I hope most corporations never experience a crisis like that of Virginia Tech on Monday. But it is a virtual truism to suggest that wireless access is quickly becoming indispensable to modern business processes. From WiFi phones to hand-held computers and scanners, from Pocket PCs to notebook computers carried to various meetings, the advantages of information at your fingertips and communications technology available anytime hardly need justification anymore.

The Virginia Tech crisis only highlights a growing realization among IT professionals. Most IT managers are beginning to reflect on how inexpensive devices might be used in corporations to improve everything from disaster responsiveness to on-the-spot job training to line-of-business information retrieval. Given the eagerness of telecommunications companies to sell smart phones in quantities to companies, you can readily imagine a situation where everyone in a company from the President to janitorial staff would be issued a joint cellular/WiFi phone. The WiFi costs would be covered by the company, while most cellular usage would be the responsibility of the user (if used at all).

When an employee comes to work, they use the device to send and receive instant messages or text messages, to read and write corporate email, to gain instant access to operating procedures and policies, training manuals and even for information access to ERP applications as required. Devices would be subject to policies preventing misuse, of course, but some kind of automated monitoring service which aggregates usage statistics would help managers determine who is doing what when and then take appropriate disciplinary measures if necessary.

I don't think this is too far fetched. After all, many families are already there with every member having his/her own cellular phone and/or computer. High tech companies are already using either blackberries or smart phones with almost 100% distribution among employees. Soon enough, the manufacturing and other industrial sectors will see the same advantages. After all, not everyone in a manufacturing company can have access to a computer. But if we could reduce costs to, say, $200 per user per annum, wouldn't the advantages be obvious?

Wednesday, April 04, 2007

Predicting IT Trends - Microsoft Databases

My family and I like to visit large bookstores together. We tend to drift apart shortly after arriving only to come together again for coffee and treats in Starbucks. I tend to head over to the science and technology section and the computer-related bookshelves, my wife to the novels, my eldest son to the gamers area, and my youngest son to the culture studies section.

One thing I like to do while perusing the computer books is to predict trends in information technology. What programming languages are getting a lot of coverage? What certifications are taking off? What popular trends are emerging in web services? What databases get the most press?

This week, I had fully intended to attend a regional Microsoft event entitled The Exciting Adventures of the Microsoft Application Platform Developer not just because it was intended for both developers and IT managers, but because I was curious about what trends were emerging in Microsoft products for data-driven applications and web sites. Unfortunately, I felt too ill to attend the event. But it still got me thinking and wondering about the future.

Why is it, for instance, that I see so little on the bookshelves about a product like SQL Server Express? I bought Rick Dobson's Beginning SQL Server 2005 Express: Database Applications with Visual Basic Express and Visual Web Developer Express, From Novice to Professional some time ago, believing that I should become conversant with a product that seemed ready to infiltrate small to medium-sized businesses who had outgrown Microsoft Access. But I haven't seen it on the shelves recently, nor any of the many SQL Server Express books available online. Based on the books lining the shelves in Chapters, I'd have to say there isn't much of a future in store for SQL Server Express.

But maybe it's just a matter of timing. Maybe it's a matter of my being interested primarily in small and medium-sized businesses. Maybe Microsoft needs to do a little more marketing. Or...just maybe Microsoft Access still can fulfill most of the requirements for departmental databases, for small- and medium-sized databases without worries about the .NET CLR, XML data types, etc. Certainly the Chapters bookshelves look more promising for Access than SQL Server Express.

Sunday, April 01, 2007

Geeks Do April Fool's Day

You always have to be on guard come April Fools' Day, especially if you're into technology, technology news, and blogging.

So what's up recently that may or may not be a joke on us geeks?


  1. Windows Vista for your Pets (OK, that's a dead give-a-way)

  2. "xxxx is a fellow IT Pro Technology Advisor from xxxx, he is very well connected to some influential people at Corp. in Redmond..."
    Nathan Mercer
    Michael J. Murphy
    Damien Caro
    Daniel van Soest
    Rodney Buike
    and so on in a ring around the blogosphere

  3. TechCrunch Has Acquired FuckedCompany.com
    Mathew Ingram's spotting the prank


The first two may be exactly the same joke. In fact, it was the Vista for your pets that kind of gave it away, especially since the format of the IT Pro Advisor blogs was almost word for word.
The problem is that, because geeks love April Fools' Day and because geeks generally don't do the joke very well, you're never quite sure. One example is Robert Scoble's joke for 2006 in which he announced he was leaving Microsoft for Google. It was kind of lame, but typical of the geek approach to April Fools'. The title was credible, given his praise of Google over the years. And in retrospect, it wasn't many months later when Scoble did leave Microsoft, not for Google but for Podtech. Hence the uncertainty.


Anil Dash did a little bashing of geek April Fools' Day jokes last year. One example was


  • "We have a big announcement today!" No you don't. It's Saturday.


Which got to to thinking about why a guest blog submission of mine wasn't being published until early next week on the IT Managers Connection Community Blog when it could easily have been published this weekend. Could it be that the entire Microsoft IT Pro Advisor network is complicit in an April Fools' Day hoax and want to keep the community blogs clear until the hoax is fully perpetrated? I don't know. Maybe I'm just way too suspicious.


But if the theme interests you, Gizmo has a list of the top ten geek pranks of all time, some of which I may consider using on my colleagues at work. Wikipedia has an even better list of jokes by media type as well as a list of genuine events mistaken as April Fools' Day hoaxes (that might be one for me if I'm wrong about the IT Pro Advisors announcement rumor).


So, whether you're a perpetrator or a jokee, have a fine April Fools' Day 2007!

Sunday, March 25, 2007

IT Managers and Bridging the Gap

If you want to be stimulated intellectually and if you prefer science and technology to a postmodernist, literary rant, then you need go now further than The Edge, a web site dedicated to The Third Culture, consisting of scientists and other thinkers in the empirical world.

IT managers are generally a practical bunch. Sure, we love delving into the frontiers of information technology, reading about the new and the wonderful, planning for a future which is always just around the corner, sometimes even wondering when we can download our consciousness into a cybernetic mechanism so that we can live forever. But, when we wake up from that good night's dreaming, we tend to check things like whether the backup worked last night, how many - if any - viruses were detected across the network, whose printer malfunctioned during the night shift, and so on.

IT manager nightmares, on the other hand, turn on that common phrase, "You just don't know what you just don't know." The meaning is fairly obvious - we manage technology daily, and to do so effectively means that we constantly have to learn. We consistently have to push down the barriers between what we know and what we don't know. We expect that just around the corner there is a small piece of critical information that will pull the entire puzzle into a coherent whole. We might not know what we don't know, but you can be damned sure that we're looking everywhere we can both to find the individual puzzle pieces and to find a way to fit them all together.

Which is why I recommend information technology aficionados read The Edge. The Third Culture promoted there is something with which most of us can immediately identify. We build bridges just like the digerati of The Edge, and in almost identical ways. But instead of building bridges between scientists working in the field of string theory or evolutionary biology and the reasonably well-educated general public, we build bridges between computer scientists and software engineers, on the one hand, and the users of our corporate information systems.

At least that's the way IT should work.

Recently, The Edge published news about one IT professional's initiative to bridge the gap. Danny Hillis has announced a new company called Metaweb and a free database called Freebase.com. The "massive, collaboratively-edited database of cross-linked data" will be an "open shared database of the world's knowledge". Licensed under the Creative Commons Attribution License, the data will be available to programmers worldwide to build services to provision the data. Imagine Google, Wikipedia, Blogs, Tags, Trusted Links - all rolled together with data that is understood and readable by computers but presented to users in a format that pleases.

That's the goal. But if you're like me when searching for that single piece of the puzzle, and not sure about what you don't know that you don't know, what is it about this bridging exercise that will make the difference? The short answer is that we don't know yet, but Hillis is banking on some combination of "emergent structure and intelligent design" in which Metaweb architects intelligently design the grammar of specifying relationships among data and the crowd creates the content in Freebase.

Hillis has been able to secure over $15 million in investment funding. The Edge digerati think it credible enough to warrant coverage. Now we wait and see.

Wednesday, March 21, 2007

Windows Server 2003 SP2 - Default Web Page in Internet Explorer 6.0

A number of users on our corporate network have brought to my attention that their default home page has switched from whatever they had set to MSN.com. This all occurred after I upgraded the operating system for several servers to Windows Server 2003 Service Pack 2.

This may be old news to many IT managers, but I was still surprised to confirm the "problem". We run terminal services and thin-client devices for most of our users; in fact, even those with notebooks and desktops access the network resources through Remote Desktop Connection. As you may know, terminal services provisions Internet Explorer browser services according to individual profiles. Thus my surprise that all users had their default home page reset to MSN.

I wonder how many network administrators write logon scripts or hack the registry to set the default web page (e.g. [HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Main] "Start Page"=http://www.panocap.com/)?

I can understand how the initial installation of an operating system will set the default home page of the browser to a Microsoft site like MSN. That's really a no-brainer. But it's not nearly so obvious to me why an update to an operating system should switch user's default home page back again. That seems to me to be a blunt marketing instrument.

Saturday, March 17, 2007

Daylight Savings Time - Aftershocks?

Let's say you're a seismologist and you develop a technique to prevent earthquakes. You take your responsibility seriously, so you invest as much time, effort, energy and money as you can muster into perfecting the technique. You go ahead and implement the technology along a fault line close to a major metropolitan area. Your technology works perfectly. You predict and prevent a major catastophe. But nobody notices.

Well, if you're an IT manager and you did your preventive maintenance well before last Sunday's daylight savings time extension, the worst thing to have happened was that your PBX-based telephone clock was off by an hour when you came into the office on Monday. I'll bet that got noticed! But nobody noticed that you prevented information system problems significant enough to have warranted a Gartner risk assessment warning.

My experience of the aftershocks of DST was exactly the same as Y2K. Nothing significant happened...at least not to the systems with which I was associated. There were, to be sure, significant problems unreported in many small- and medium-sized businesses. In fact, I know firsthand of at least one company whose demise was related to non-compliant Y2K systems. And I have heard stories of other organizations whose preparedness for the DST extensions weren't as comprehensive as they should have been. Some of the stories are truly funny.

But...at least if you encountered some disruptions owing to the DST extensions, then IT gets recognized. If you were perfectly prepared, nobody notices, no thanks are offered, no congratulations are given. It's as if you did absolutely nothing.

Don't get me wrong. I'm not suggesting that IT pros become less professional. But maybe it's time we start "educating" users more thoroughly. You can be sure that marketing professionals wouldn't stand idly by without getting clear acknowledgement for their work. Maybe it's time we take a page from their notebooks!

Sunday, March 11, 2007

Identity Theft, Portable Drives and IT Responsibility

I've been thinking recently about how much responsibility IT Managers should assume. True, it seems that every day there is another "issue" which arises for SMBs (small to medium businesses) in which information technology has a role. Disparate systems converge. Silos of information need to be managed. Whether it's real-time monitoring of machines in the factory, implementation of VoIP telephony, deployment of biometric time-and-attendance systems, coordination of video and audio resources, or automation of physical security systems, the IT manager constantly has his or her domain of responsibilities increasing. Not bad if all you care about is expanding an empire. But a little intimidating if all you get is an ever-expanding job description with no pay raise.

My take on this is simple. It comes with the territory. Expansion of the domain of IT responsibilities is inevitable. The only feasible approach is be proactive and realize that management tools will emerge to fill the vacuum. But the expansion of responsibilities is also part of the challenge of being an IT manager and one of its truly fascinating opportunities. Each day presents a chance to know a little more about a technology which was previously slightly mysterious and which will now be managed.

Here's a case in point. I'm hoping readers will jump in with other examples and differences of opinion.

We've all witnessed an explosion of portable drive technology in the last few years. We've also seen, almost daily, news stories about identity theft and the exposure of private information. One recent example in Canada was the theft of customer information from Winners and HomeSense (through computer information systems belonging to their parent company TJX Cos in the United States). Another example was the loss of a computer with about half a million Talvest Mutual Funds client accounts from CIBC. In the United States, the Veterans Administration was breached with a loss of up to 1.85 million records.

Whether the losses occurred through computer theft, hacking systems, or plain, old user stupidity, they all involve questions of the extent of IT manager responsibility. If you are constantly looking over your shoulder worried about losing your job, then it is highly likely that you will want to limit your responsibilities and divest yourself of whatever you can. If, however, you are fortunate enough to feel relatively secure in your job and are motivated primarily by the challenge of solving problems, then you will be thinking about how to mitigate risks and exposure. Those differences in attitude are, in my view, huge. Anything you can do to get into the mindset of solving problems with technology rather than limiting personal exposure is guaranteed to improve your job satisfaction.

One small thing IT managers in SMBs can do in 2007 to mitigate identity theft specifically and data theft generally is to implement fingerprint biometrics or multi-factor authentication wherever possible. Start small with portable drives. Ensuring that these units are standardized in your company and that they are reasonably secure will reduce your exposure.

I come from a large family with several siblings working in the IT sector. We've recently discussed in our family e-group all the differing smart/thumb drives and portable drives we are using. It quickly became apparent to me that if we can have this much diversity in a family, how much more can we expect among users in our companies?

Standardizing on a fingerprint biometric flash memory drive (I've seen a few Microsoft IT Pro advisors with these units) is the first step. iQBio has a variety of units that are worth considering. The 2GB ClipBio "flip clip" is both weatherproof and fingerprint biometric enabled. Up to ten fingerprints can be enrolled per device. By ensuring only specific devices for portable storage are allowed in the company, you can mitigate risk of theft slightly.

Migrating to Windows Vista and implementing Group Policies to block unwanted devices while selectively enabling others would also mitigate risk. But the added benefit here is that you can actually boost performance on those Vista systems with ReadyBoost technology. The idea is that USB flash drives can be used to give the memory on your system a boost thereby enabling memory-intensive GUI features.

I'm sure readers will have other opportunities in mind for mitigating data theft exposure. But my overall point remains. Embrace the challenge, protect your company's information assets, and make management slightly easier through standardization and group policy implementation.

Wednesday, February 28, 2007

Mind Mapping Daylight Savings Time

Monday evening, I had the opportunity to talk to a group of fellow IT professionals at the Waterloo-Wellington IT Professional User Group about using mind mapping software for IT management tasks. Ruth Morton, IT Pro Advisor with Microsoft Canada, wrote about the presentation on the IT Managers Connection blog.

During the presentation, we did a brainstorming session to illustrate the utility of mind mapping software to quickly capture ideas in a group setting and to then organize those ideas into a form ready for further research and investigation. The group chose the perfect subject for IT pros - the implementation of the new daylight savings time seasonal extension on operating systems and application software platforms.

I took a blog entry from another Microsoft IT Pro Advisor, Rick Claus, who was in turn forwarding information from another Microsoft Canada Technical Account Manager, Pierre Roman, with the latter's gathered wisdom about DST, and mapped it. The result is shown in the accompanying map. Unfortunately, much of the functionality of the map is entirely hidden here, such as the hyperlinks to the relevant Microsoft knowledgebase articles or the text notes which automatically popup when you hover your mouse over the topic.

Blog entries like this can only tease the reader into investigating mind mapping further. They can't come close to illustrating the amazing richness of the feature set. To do that adequately, the user would have to download the map as well as a free viewer (Mindjet's viewer can be downloaded here). I hope to have this particular mind map available online soon to share with other IT professionals (until then, if you would like a copy, email me privately and I'll forward a zipped copy of the file).

In my view, there is absolutely no other software category that comes close to mind mapping for presenting information in a "big picture" context. The reader of a mind map automatically gets a sense of the relationships of ideas and concepts.

But it is in generating ideas, collaborating with others, editing and rearranging, and linking concepts and ideas that mind mapping truly shines.

Daylight savings time is meant to save energy on the macro level. Mind mapping does that on a micro level; but it does so much more. Finally, it appears that the world of software is catching on. Do a simply Google search on "mind mapping software" and it will quickly become apparent that the category is exploding in interest and products available. MindManager Pro 6 (from MindJet), iMindMap, NovaMind, Visual Mind, MindMapper, MindGenius, BrainMine - these are only some of the products now available. If you want a blog dedicated just to mind mapping software, you can do no better than Chuck Frey's The Mind Mapping Software Weblog.

Save your time. Save your energy. Try mind mapping.

Hands In My Pocket

Jim Guthrie wrote a very catchy ditty for Capital One's marketing campaign for Canadian TV. You can listen to an extended version on YouTube that has nothing whatsoever to do with the marketing campaign. TrendHunter online magazine also has a decent article about the genesis and rationale for the ad campaign. Whatever the merits of the campaign or the music, the jingle embeds itself like a virus in your subconscious.

But what got me thinking about the jingle this week - apart from watching too much TV of course - was receipt in the mail of the prize I won from Podtech for a blog writing contest on why I needed more computer storage. The prize was a Seagate 8 GB pocket drive.

What a slick, well-designed, and useful device! 8 GB in my pocket!

Once I told a few friends at work about the prize, it was a no-brainer that I'd have to make sure there weren't any hands creeping into my pockets to steal this little baby. Perhaps I should have kept it a secret. It looks good and it works even better.

In my part-time custom application development business, I often have to transfer large files back and forth, files too large for email and sometimes too large even for FTP site transfers. Now with the Seagate pocket drive, those files can be safely copied in a matter of moments. True, I have to visit my customer to do this, but that is something I need to do anyway in order to discuss enhancements and upgrades. Where physical copying of files is a likelihood or necessity, the pocket drive is the best solution I've seen yet. No power cords, no clunky external drives requiring special software to install on the client computers, just a USB hide-away connector.

File transfer and backup is really only the start to this device's usefulness. What really sold me was the ability to install applications on the pocket drive while connected to a thin-client notebook (the Neoware m100). I did a minimal install of Microsoft Office 2003 and was very pleased to see that the performance was very good. The Neoware m100 is designed for mobile thin-client computing, which means that unless there is a wired or wireless network readily available, the device cannot be used for always-ready applications. But with the pocket drive, the mobile thin-client can be used in a similar fashion to an everyday notebook computer, without the attendant problems of malware protection, data theft, etc. True, you have to protect the pocket drive, but the device comes with software which does exactly that.

I suppose in another few years I'll look back and think "how quaint" just as I do now nostalgically recalling my very first 5MB removable hard drive I had for the original IBM PC in 1985. Ah, good time...good times! But for now, it's cool, very cool!

Thursday, February 22, 2007

Thin-Client Computing on the Move

Neoware is making it possible to have the security and ease-of-use of thin-client computing on a mobile platform. The recently released m100 looks like any other notebook computer except for a couple things. There is no hard drive and no CD-ROM - just a keyboard and screen, a Windows XPe operating system, and some management utilities. If a road warrior loses the m100 or if it's stolen, the only true loss is the price of the unit. There is no exposure of sensitive data. True, without Ethernet wired or wireless connectivity, the unit isn't useable for word processing, spreadsheets, databases, or anything else that might be possible with a standard notebook computer or tablet PC. But more needs to be said, I think.

I couldn't get over how simple it was to get the unit configured for use - 10 minutes from opening the carton containing the unit, it was ready for use on our corporate network, both wired and wirelessly. After taking the unit home in the evening, it took only a few minutes to configure the WEP key, connect the Windows Media Player to an online jazz station and connect through Remote Desktop to our corporate network.


Security is unparalleled. IT management couldn't be simpler. No viruses to worry about, no worms, no rootkits - no malware period! No moving parts to malfunction. It couldn't be quieter (except when Windows Media Player is running, of course). A VPN client can be installed if necessary, but everything else is ready to go right out of the box. No training required since almost everyone using units like this will already be acquainted with Windows XP.


But should you need to take some notes when no connectivity or VPN access is available, there is still Notepad. If you want to take along some music, photographs, or videos with you while on the road, there is still USB connectivity. If you want to read PDF files (or books, for that matter), Adobe Reader is already installed and ready to go. In my test, for instance, I connected a 1GB memory stick that contained an entire set of IT manager-related documents from Tech Republic in PDF format. No problem! In additionn, while that smart stick was still connected in one of the five, count 'em, five USB ports, I connected my 8GB Seagate pocket drive and accessed JPG and HTML files. I could just as easily have watched a movie or two.


There are audio in and out jacks, a modem port, 6 hours of battery life, a port for an external monitor, 2 stereo speakers, and one PCMCIA type II slot. The modem port is old school, to be sure; it would have been much cooler if bluetooth or infrared ports were available to use along with a Smart Phone or phone-enabled Pocket PC for those rare occasions when you need connectivity but no Ethernet networks are available. But overall, if you don't need always-ready, always-available applications and data, this sweet little unit provides almost all you need while on the road.


In the office, especially offices with wireless connectivity available, it gets even better. You can easily take the unit with you to conference rooms or meeting rooms or a colleague's office, take notes, use all the server-provisioned applications available, work online or anything else that you would do while tethered to the desk in your office.


But most importantly, if you want to make your IT staff happy - and who wouldn't? - consider mobile thin-client computing...please! (This entry, including saving a copy of the photo above, was all done on the m100)

Sunday, February 18, 2007

Spam that kills

If you get spam, you've probably received some, perhaps many, of these spam messages before. They purport that you are eligible for an inheritance transfer. Most of the time, the message indicates that your name was part of a search linking you somehow to the person who died. Again, most of the time, there is no apparent rationale for the linkage apart from the claim of the spam artist sending the email. So, you simply hit the delete key and move on, no matter how many millions of dollars are supposedly available in the "dormant" account of the deceased person.

But what if you received a message about an inheritance transfer that said your brother or sister had passed away and that you are named in the will? Would it be as easy to hit the delete key, especially if you live in another part of the world and haven't seen or spoken to your relative in a few months or years? What if the person named didn't have a will - and you happen to know this as well - and that you were discovered in a last name search? What if your name is uncommon and the person named as the deceased does have the same first name as a close relative? What if the email doesn't make extravagant claims about $30,000,000 million in American funds? What if it doesn't even mention the amount available, but instead simply suggests that a certain percentage will go towards legal costs in securing the inheritance for you?

You've probably already figured out that this sounds a lot like the Nigerian 419 spam. But this one comes from England or some other part of the world.

The variations on this spam/scam are endless. Unfortunately, it's becoming more sophisticated all the time. The particular example I'm giving came to me from a colleague at work who life was put into temporary turmoil because he did, indeed, have a brother whom he hadn't seen for a while and who might possibly have died.

It was probably only a coincidence. His brother is alive and well. It was probably only a case of a generic Nigerian 419 spam email message that just happened to have more plausibility that other variants. But in his case, we're talking about spam that kills your brother and then asks if you want part of the inheritance. It can't get much worse than that.

Wednesday, February 14, 2007

SWAG meister

One of the nicknames I have at work is "the Don Meister". All it means, of course, is Don, the Master. One can hope it's used affectionately to denote the one with the the keys to information technology heaven and hell, a kind of St. Peter ordinaire, not at the pearly gates, but at the gateway to that awesome computer screen phenomenon of "hey, that was easy!"

But being associated with the computer industry now for over 20 years, I've come to appreciate being a meister of SWAG - sometimes known as "Stuff We All Get". SWAG is promotional items that you get from companies or organizations by virtue of participating in a seminar, a course, a conference, or some other kind of event. Over the years, I've done fairly well. Not all SWAG is received by everyone, of course. Very often, it's the result of a draw.

What have I won? A notebook computer, a keyboard, a few backpacks or tote bags, toques, T-shirts, sweatshirts, paper weights, squeeze balls, pens, pencils, notepads, USB memory sticks, external storage devices, even blankets. Spread out over 20 years, it hardly seems noticeable, but when you take stock and itemize the collection, you realize just how much has actually come your way by participating in promotional and training events. In the last month, for instance, I have won prizes from Podtech (sponsored by Seagate) and another from Microsoft Canada. Nothing worth gloating about, but certainly bright spots on cold winter days when the sun might not be shining.

Some SWAG I've received has come to me by virtue of being an employee. Pano Cap has given me T-shirts and lunch bags, for example.

Sometimes SWAG is controversial. Some companies require that all employees ensure gifts they receive from suppliers and partners are under a certain monetary value (I'm assuming that doesn't include prizes won in a draw). Some bloggers (people like Robert Scoble, for instance) get so much SWAG that they make a point of publicly declaring everything that comes their way, whether they accept it or not.

But most of the time for most of us, SWAG is not too controversial. It's just a pleasant, occasional aspect of being part of a professional community, a member of an association, or an employee of a company.


Sunday, January 21, 2007

Codes of Ethics - What History Has To Offer

I have the good fortune of working in a company that has a code of ethics (or conduct). It is also a multicultural, multiethnic company. It is a company which prides itself on its environmental awareness and its commitment to business and personal integrity - in other words, a company of which I can be proud.

Corporate codes of ethics, as well as many statements of principles in government organizations, bills of rights and freedoms - they all generally state their belief in equality and their opposition to discrimination. But we all know that nation states, companies, and individuals in even the most inclusive and tolerant societies harbor racist and bigoted attitudes. It's not just that a few people disagree with the bills of rights, but keep that opinion to themselves. The far more insidious problem is that the vast majority consciously agree with the statement of principles and yet unconsciously display racial behavior and stereotypical opinions.


Jared Diamond believes that education is the solution, especially a large historical overview of human civilization. Education, in this case, means being very clear about the nature of the problem and offering a logical and satisfying answer.

Here's part of the problem. We all know that Eurasians conquered the known world in the last 500 years. Does that mean that Africans, aboriginals, and native North Americans were somehow inferior? I mean, why didn't they beat back the invading European colonialists or cause epidemics to decimate the conquerors rather than the other way around?

Technology is one answer. Those who won had better tools. But if we go back, say to 11,000 B.C., every human society had roughly the same technology and sophistication. Why, over the course of 13,000 years did the Europeans advance so quickly? Historians generally don't have anything to say about this because they are afraid of being labeled racist. But the problem with the silence is that most people assume the answer must have something to do with biology or average IQ level.

This is tough stuff! Diamond believes that the reason racism continues is simply because nobody is proposing a better answer to the often unspoken question. But in his view, advances in our knowledge of molecular biology, plant and animal genetics and biogeography, archeology, and linguistics supply a far more satisfying answer, one that offers the prospect of providing the context for our honorable national and company codes of ethics.

Diamond won a Pulitzer Prize in non-fiction for his book Guns, Germs and Steel: The Fates of Human Societies in 1998 which outlines what I find to be a very satisfying answer. It is not a definitive answer, mind you (I am finding recently that a theme of good enough or asymptotic reasoning has emerged in my research and writing), but an indicative answer and one that may prove to be more compelling that the lower IQ, less-gifted assumptions many people hold.

Here's the short answer: it's an accident; it's all about luck. There is no inherent superiority among the world's races. Instead, the reason why Eurasians were so successful so quickly is because they had an abundance of domesticated crops and animals and because the east-west orientation of the land mass made the transfer of animals, crops, and technology easy. Bill Gates offers a summary review of Diamond's book which is easily consumed in a few minutes of reading.

My point here is simply to suggest that codes of ethics are important, but more important still is a broad understanding of the history of technology which illustrates how luck and accident account for those distressing inequalities which our codes of ethics seek to mitigate. And, as Bill Gates says, in our age of information technology, luck and accident are not nearly as important as intelligence, skill, and leadership.

Wednesday, January 17, 2007

Making IT 'Good Enough'

  • I've been guilty of this before, and I'll undoubtedly be guilty in the future - going for the gold standard, striving for excellence, discovering and emulating best practices. But maybe in IT, doing so isn't always appropriate. Maybe it can be a misguided approach.

    Here's just one example. In the past few years, IT gurus have developed process frameworks and control frameworks in order to provide all companies - big, medium, and small - with best practices for IT management. All conscientious IT managers and CIOs want to be part of the select group of businesses who are doing IT right. It's a matter of professional pride and the automatic assumption that best practices will improve not only IT management but business performance too. From CoBIT to ITIL, from security mantras like "defense in depth" to regulatory compliance like SOX, IT managers are bombarded with calls for better management. Often, we assume that means best practices. But that assumption may be part of the problem.

    Best practices are, by definition, ideals. But when money is tight (and when isn't it?), doing more with less may mean going for bronze rather than gold. Sometimes, it makes more sense to aim for a 7 rather than a 10. Sometimes, taking steps to go to the next level just isn't cost-effective. Sometimes, aligning IT with business objectives means intentionally going for the good-enough solution rather than the perfect solution.

    CoBIT (Control Objectives for Information and Related Technology) and ITIL (Information Technology Infrastructure Library) provide so many markers for IT performance that IT management can become disoriented and lose sight of "key" performance indicators. These frameworks can still be useful, but leveraging them may mean incorporating home-grown measures and concentrating on fewer key performance indicators.

    The IT Controls Benchmark Survey, for instance, provided some surprising results. The smoking gun for top performers could be found in 2 measures, measures that the best-of-the-best were almost all doing and that almost all the also-ran were not doing:
  • Monitoring systems for unauthorized changes, and
  • Defining consequences for intentional unauthorized changes.
    What this means is simply that, while ITIL and CoBIT give a lot of good measures to consider, the biggest bang for the buck comes from concentrating on doing a few things well.

    The survey also showed that in manufacturing, the top performers were about twice as productive as the low performers. But in IT, the difference was five to eight times. It is a case of the 80/20 rule again. Eighty percent of the benefit on process and control frameworks come from twenty percent of the measures.

    With survey results like this, achieving excellence in IT may be more about being "good enough" than in following "best practices", or at least about doing a few key things really well, and the rest just good enough.

Thursday, January 11, 2007

The Invasion Continues

The Economist had a very interesting article in its Work-Life Balance Computing article of 19-Dec-2006 entitled "Consumer technologies are invading corporate computing."

The gist of the column, like so many articles over the past few months about the impact of consumer computing on IT, is that corporate computing departments can't hope to keep up with the advances in consumer electronics, web-services, and other consumer-focused technical advances. This time the case-study involved a forward-looking IT Manager for Arkansas State University who moved student email from the university servers to Google.

65,000 students are having their email accounts transferred at the rate of 300 per hour to Gmail while retaining the university's domain of asu.edu. They get web-based email at no additional cost to the university, along with instant messaging, and shared calendars. Not a bad deal!

But what really sets this IT Manager apart is his rationale for the move. He knows that the pace of consumer-driven technical change isn't something that corporate environments can match easily. But companies like Google can introduce web-based services like Google Apps for Your Domain (which, by the way, is still in beta), and then add new services like word processing and spreadsheets, or wikis and blogs without requiring the legions of technical support staff that rolling out new services like that in a corporate environment would require.

What about security and backup? Again, corporate IT departments need not worry. One of Google's data centres burnt to the ground - but nobody noticed! Because the other data centres picked up the slack and continued to provide the service required. Massive redundancy and massive storage capacity means that Google can offer these web-based services without compromising security and backup.

You can bet I will be watching developments like this very carefully over the next few months!

Wednesday, January 10, 2007

iForgot Who iAm

It's been fun to read the various news articles and blog entries about the Computer Electronics Show (CES) in Las Vegas this week as well as Macworld in San Francisco. You might wonder why Apple would decide to host its conference at the same time as CES, but then all you have to do is ask yourself what the biggest consumer electronics announcement of the week was - that's right, the iPhone and iTV. In addition, Apple dropped the word "Computer" from their corporate name this week.

Clearly, Steve Jobs and Apple are moving the standard markers for the company and are seemingly successful in doing so. If the pundits are right about what the future will bring for IT managers - consumer electronics, applications, and sensibilities into the corporate environment - then, Apple may simply be on the vanguard of that movement. Still, the phrase "stick to the knitting" comes to mind, meaning businesses should normally stay with the brands and business for which they have become known. In Apple's case, that would be personal computers for the "creative" and "artsy" end of the market.

Whatever opinion you might have about Apple and its future, consumer electronics is obviously changing our vocabulary. There was a recent comical example of that on the television hit drama House in which the character played by John Larroquette wakes from a coma and is reading about something he has never seen before, something called an "iPod" (which he pronounced with a short i).

Even if you've never been in a coma, even if you've merely been asleep for a few hours, chances are something new in consumer electronics has happened overnight that your teenagers can tell you about. My sons, for instance, stay up much later than do I each evening. In the morning, when I drive them to school or university, they usually have something new to tell me about from listening to a podcast or watching a technology show on digital television. It's a rare morning now, when I can surprise them or I don't hear a new word entering our vocabulary drawn from that massive realm of consumer electronics.

Sunday, January 07, 2007

Stay Tuned

2007 will see me assuming some additional responsibilities at Pano Cap. I will be assuming roles as editor for a resurrected internal newsletter as well as web master for our corporate web site. I look forward to both. Although our Pano Post Newsletter is for internal consumption only, it will be a welcome improvement in communications. I'll also enjoying stretching my skill set into print publication software as well as refreshing my editorial experience, something I haven't done with any frequency since my graduate school days.

The Pano Cap Canada web site, partially because it is directed to both an internal and external readsership, will be more of a challenge. We have been somewhat negligent in keeping our corporate web site current and dynamic. That will now change.

I have developed and taught courses at Conestoga College in creating and maintaining database-driven web sites, but it is has been quite a while since I've had hands-on web-master duties to perform regularly. Again, I anticipate not only helping with content creation but in learning about the most current tools and techniques available for web site design and maintenance. One piece of software I will probably try out during the next month is Adobe's Dreamweaver 8. Right now, it's a toss up whether to go with this standard in web design or whether to try Microsoft's most recent professional entry into this market - Microsoft Expression Web.

Suggestions are always welcomed.

Monday, November 20, 2006

Hugs & Kisses, Hurts & Curses

Norman Nie of Stanford University says, "You can't get a hug or a kiss over the Internet." (Social Intelligence: The New Science of Human Relationships, p. 9).

Daniel Goleman, the author of the 1995 best-seller Emotional Intelligence, has authored a new book which I hope every IT Manager makes time to read, Social intelligence. The point of the book is that we are all "wired to connect", no matter how much technology is part of our everyday experience. In fact, in the beginning of the book, it is clear that Goleman believes recent technological developments are insulating most of us from that essential human connectivity for which we are biologically wired. From the car, to the cell phone, to the iPod, Goleman argues we are encasing ourselves in technology which isolates us from one another, leading to what he calls social autism.

Stephen Covey made a similar point in his book First Things First (1996) when he said, "You can be efficient with things, but you need to be effective with people, particularly on jugular issues." I've remembered that point over the years, but it bears repetition. With Goleman's new book, not only is the point repeated, it is reinforced with research from the the new discipline of social neuroscience. Our emotions and moods are all about human connectivity and the jugular issues of communication.

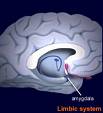
In the opening chapters, for instance, he talks metaphorically about the high road and the low road of communication. The high road is all about the frontal lobe of the brain, the location where reflection and rationality intercede, hopefully stopping us from saying something stupid. The low road, on the other hand, is all about the amygdala, almond-shaped groups of neurons buried deep within the temporal lobes of the brain where we sense one another's mood and emotions before we have had time to reflect or rationalize. The salient point is that the low road works far, far faster than the high road.

We experience this whenever we watch a movie or are engaged in a conversation with someone and intuit something going on. Whenever there is a hint of a smile on someone's face and we respond with our own smile or, even in a more subtle fashion, with a minor shift in mood which mirrors that of our conversationalist. All of this happens in an instant and before we are aware of what is going on consciously. This means, of course, that there is far too much information in one-on-one conversation to rely on e-mail, instant messaging, blogs, or other forms of communication which technophiles, like IT managers, use and promote everyday.

We may not hug or kiss one another in such conversations, but the point is still valid. The wiring we use for our technology cannot, and perhaps never will be, as effective in communicating with one another as the face-first conversation.

Sunday, November 19, 2006

Spam, Botnets, Pump-and-Dump, and Armageddon


Spam has become such a common part of life with e-mail these days that even bringing up the topic in casual conversation has become boring. Boring, that is, unless the conversationalist brings something novel and interesting to the dialogue. If that's true for casual conversations, then it's absolutely true for blogs and other forms of monologue.

Maybe considering volume and percentages helps. I estimate that I receive about 120 spam e-mail messages daily on my personal e-mail account. Because my corporate account is pre-laundered by an external service before e-mail arrives in my Inbox, it's a little more difficult to discuss absolute numbers and percentages (we use Postini's Enterprise Email Protection Service). About 52% of our corporate e-mail is either blocked or quarantined for further review.

My experiences reflect the overall historical situation. In 1978, an e-mail spam was sent to 600 addresses. By 1994, the first large-scale e-mail spam was sent to 6000 bulletin boards and eventually reached millions of people. By June 2005, the volume of spam had reached 30 billion per day. By June of 2006, that number had risen to 55 billion spam e-mail messages per day. About 80-85% of all e-mail messages globally are now "abusive" e-mail (see e-mail spam on Wikipedia).

OK, so maybe even talking about absolute numbers and percentages aren't all that interesting. What I do find interesting, though, is that digging a little deeper into the phenomenon of spam demonstrates alarming changes that go well beyond simple numbers. I'm thinking here of botnets, so-called pump-and-dump, international e-mail crime gangs, and the advent of Armageddon.

Here's a recent example. In the past few weeks, there has been a surge of spam for penny stocks and penis enlargement pills. Evidently, the surge has been tracked back to a gang of Russian hackers who have cobbled together a botnet of 70,000 peer-to-peer computers is as many as 160 countries worldwide which uses the SpamThru Trojan to do the dirty work. Botnets are "broadband-enabled PCs, hijacked during virus and worm attacks and seeded with software that connects back to a server to receive communications from a remote attacker" (Is the Botnet Battle Already Lost?, 16-Oct-2006, eWeek). Computers controlled through botnet technology are generally called zombies. They provide the mechanism whereby spam is generated and delivered, bringing back billions of dollars in revenues to the gangsters.

How prevalent and dangerous is the threat? Since January 2005, Microsoft's Malicious Software Removal Tool has removed at least one Trojan or bot from 3.5 million individual computers. When those computers were compromised by the hidden code, they exemplified the first of the 10 Immutable Laws of Security: Law #1: If a bad guy can persuade you to run his program on your computer, it's not your computer anymore.

How does the bot herder get you to run his program on your computer? Through either a vulnerability on your computer or through a weak password. As Jesper Johannson says, "The only thing that stands between attackers and the end of the world is a password." (see Assessing Network Security, p. 11).

It may be a little early to tell whether the good guys can fight back and delay the advent of Armageddon. But it is clearly the case that the sophistication of the bad guys is alarming. The SpamThru trojan, for example, is not only being used in a very effective spam campaign, it is also evidence of malware that is as complex and feature-rich as many commercial software programs. This trojan, for example, has its very own anti-virus scanner embedded within its code - a pirated version of the Kaspersky AntiVirus for WinGate. The AV scanner is used by the trojan to eliminate rival malware files that would get in the way of maximizing the volume of spam e-mail sent from the zombie computer. That is very clever and very disturbing.

The SpamThru trojan also uses templates downloaded to the zombie but which uses challenge-and-response authentication methods to prevent other malware software from stealing the templates it uses from the template server. Not only is that clever and disturbing, it might even be worthy of a conversation around the water cooler on Monday.

Friday, November 17, 2006

Multifactor Authentication - It's Coming Sooner Than We Think

It's hard to believe, but it's been 2 years since the Bush administration in the United States issued the Homeland Security Presidential Directive 12. The point of the directive was to enhance security through the reduction of identity fraud. One of the ways the HSPD-12 has affected information technology is by accelerating the adoption of smart cards. In fact, ActivIdentity predicts that between 50 and 100 million smart cards will be in circulation in the United Stated in as little as 10 years.

One of my colleagues just returned from training into FPA-SAFE, a program designed to help the food industry with its audit needs. He confirmed that identity security was an important part of the training materials and concerns. He even shared some humorous stories about the lack of appropriate standards for authentication in the food industry.

This occurred at the end of a meeting in which we discussed our own internal security procedures and standards. I had introduced staff to multifactor authentication, something I had been reading about in Jesper Johannsson and Steve Riley's book Protect Your Windows Network: From Perimeter To Data. The idea behind multifactor authentication is that we can enhance identity security in computer systems by utilizing 2 of 3 classes of authentication factors: something the user is, something the user has, or something the user knows. The first usually involves biometrics, the second something like a security token or smart card, and the third something like a password, pass phrase, or PIN. By using 2 of the 3 factors, we can dramatically improve the security of our systems while making life easier for our users.

Normally, I would have thought that multifactor authentication was simply too advanced and too rich for smaller companies like ours. But international standards organization and compliance regulations are spurring growth of the technology, reducing price points and increasing the likelihood that small- and medium-sized businesses will see the business benefits of the technology.